
PHP flaw puts 70% of the internet at risk
What happened, why it matters, and how the world responded
Translated from Dhivehi. Read the original (ދިވެހިން)
20 October turned into a day of alarm for many in cybersecurity. That was when it became public that PHP, the programming language used to build about 70% of the websites on the internet, had a serious security flaw.
The news was followed by reports of governments around the world hurriedly taking their agencies' PHP-based websites offline in case they came under attack.
PHP's developers released new patches to fix the problems on Wednesday, along with a security advisory urging anyone running applications built with the language to update their systems immediately.
Why is this such a big problem?
PHP is a language for building software. Created in the 1990s, it is an open-source, server-side programming language. People in the software industry estimate that 70% of websites on the internet are built with PHP. They include many online shops, government portals and platforms such as WordPress, Joomla and Drupal, which are used to build huge numbers of websites. MediaWiki, the software behind Wikipedia, also uses PHP.
So many websites are built on PHP that a serious flaw in the language puts many millions of websites and applications at risk. It is like a key that opens all these platforms being made public: a single key that could open a vast number of doors.
The vulnerability could let hackers run malicious code on servers and access the data stored on them, putting those systems at risk.
What makes it more dangerous still is that, after the vulnerability was announced, people trying to break into systems moved very quickly. Reports say such attempts had been seen even before the official announcement.
The flaw is in PHP's core, at its deepest level. It is not a problem in a particular website, plugin or application, so updating a WordPress plugin or fixing an application's own code does not fix the PHP software underneath. As some have pointed out, even systems that are otherwise completely secure could be affected by this flaw in the PHP code they run on.
How it unfolded
In fact, the problem had been under discussion for three months before it was made public.
August 2026: a flaw hidden for years is found
In August, security researchers using AI to check code found two serious flaws, named PHP2Shell. Both were rated 9.2 out of 10 on the standard severity scale, so both were classed as "critical".
Remarkably, the flaws had been hidden in PHP's code for 10 years without anyone noticing.
As Al Jazeera reported, the cybersecurity company Calif, which works with OpenAI, reported the first vulnerability on 11 August. Wiz, a security company owned by Google's parent company Alphabet, reported the second on 24 August.
August–October 2026: time to fix it in secret
The security teams that found the problem kept it quiet to give the PHP team time to prepare a patch. This is the usual practice when such flaws are found, so that protection is ready before hackers learn of them.
17 October 2026: a warning that hackers were trying to exploit it
Four days before the planned announcement, Amazon's head of security reported that hackers had discovered the flaw and were trying to take advantage of it.
20 October 2026: details leak
Before the official updates were fully ready, details of the flaw leaked online, forcing the engineers working on the fix to hurry.
21 October 2026: emergency measures around the world
On Thursday this week, PHP's developers published details of the problem, released the patches and issued a security warning. Because of the leak, the patches came out a day earlier than planned.
In the United States, the NSA also issued an urgent warning to PHP users.
How others responded
Companies and governments around the world took many websites offline as a precaution. According to Reuters, online services and websites were temporarily taken down in Germany, France, Belgium, the Netherlands, Finland, the Czech Republic and Japan.
The Netherlands' national cybersecurity agency temporarily took systems offline to protect them, including applications at the country's main ports, hospitals and some political parties' websites.
Government networks and office websites in Finland, France and Belgium were temporarily switched to maintenance mode.
South Korea raised its national cybersecurity alert level and told more than 28,000 companies and data centres to secure their systems.
Some well-known sites, such as Wikipedia and the Internet Archive, also temporarily shut down parts of their systems until the updates were installed.
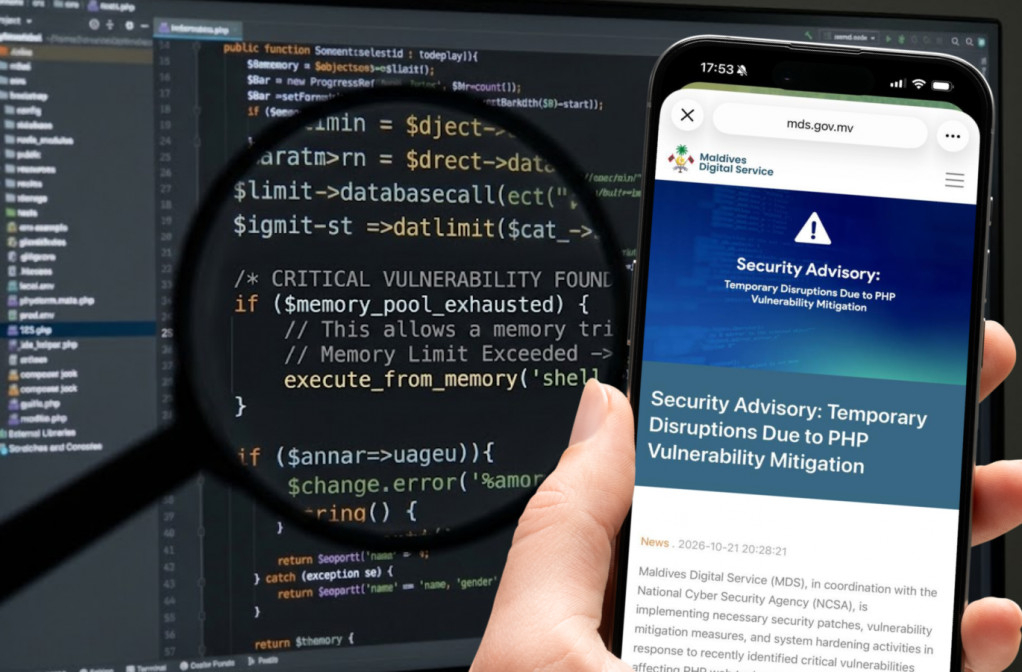
In the Maldives, the National Cyber Security Agency (NCSA) and Maldives Digital Services (MDS) jointly issued a security advisory on 22 October. It said steps were being taken to protect government digital services, and that those services could be temporarily disrupted while updates were applied.
Taking services and websites offline in this way does not mean all those systems were affected or hacked. Many organisations did it as a precaution, to assess the risks to their systems and to install updates and patches.
Even so, there were reports of rapid attempts to attack some systems. Cloudflare's CEO, Matthew Prince, said the company saw thousands of attempts to hack systems starting about 10 hours before the PHP Foundation's announcement. More than 10,000 attack attempts were recorded within 45 minutes of the announcement, rising to 100,000 within two hours and to a million by the time Prince posted about it. Amazon's security monitoring teams also reported widespread hacking activity.
These figures count attempted attacks, not successful hacks. But they show how quickly attackers moved once details of a critical vulnerability were out.
The latest reports say IT teams at many companies around the world are working non-stop to update and secure their servers running PHP.
The incident shows AI being put to good use in finding security flaws in applications: a flaw that no one had found in 10 years was discovered with the help of AI.
On the other hand, hackers are also using AI to launch dangerous attacks, and that too needs serious attention.